
To build a solid cybersecurity strategy for business, organize your plan into two parts: Left of Boom (prevention before an incident) and Right of Boom (response and recovery after), so you can reduce risk, react quickly, and get back to work fast.
If you run a business around Panama City, you don’t have time for tech buzzwords—you need a simple plan that works. The Left/Right of Boom model gives you a clear way to prepare for problems and to recover if something slips through. Here’s how to set it up.
What “Left of Boom” and “Right of Boom” Mean
Think of “the boom” as a security incident. Left of Boom covers everything you do to prevent trouble in the first place. Right of Boom is what happens after an incident—how you limit damage, restore operations, and learn from it.
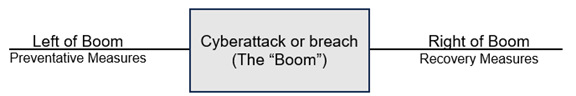
You need both sides. Prevention lowers your odds of an attack landing. Recovery planning helps you bounce back if one does.
Left of Boom: Stop Trouble Before It Starts
Teach your team the basics
People are your first line of defense. Short, regular training helps employees spot phishing, avoid social engineering, and use safer habits online. Well-run security awareness training can cut the chance of someone falling for a phishing scam by 75%.
Control who can access what
Limit access so staff only see what they need for their jobs. Strong access control makes it harder for attackers to move around if they get in. Build your approach around:
- Least-privilege access (only the permissions required, nothing extra)
- Two-step login (multi-factor authentication) on accounts that matter
- Context-based access (adjust access by device, location, and risk)
- Single sign-on to reduce password sprawl
Keep software updated and patched
Out-of-date apps and systems are easy targets. Apply updates and security patches promptly. Automated patching helps close known holes faster and shrinks the window attackers can use.
Protect your network
Use firewalls and intrusion detection/prevention to watch traffic and block suspicious activity. Lock down network settings to prevent unauthorized connections and keep sensitive data away from public-facing areas.
Test for weaknesses regularly
Schedule security reviews and vulnerability scans to find and fix issues before someone else does. Periodic penetration tests simulate real attacks so you can see how your defenses hold up and where to improve.
Right of Boom: Recover Quickly and Reduce Damage
Build a clear incident response plan
Write down what to do if something goes wrong, who does it, and in what order. Your plan should cover:
- How and when you communicate (internally and with customers/partners)
- Steps to contain the issue and prevent it from spreading
- Actions to restore systems and data safely
- IT contact details for fast coordination
Practice the plan and update it as your business changes.
Back up data and plan for disasters
Regular, automated backups are essential. Test that you can restore quickly. A disaster recovery plan outlines how you’ll bring critical systems back online and keep essential work moving.
Investigate and improve
After an incident, perform a forensic review. Learn how it happened, what was affected, and which gaps were used. Turn those lessons into concrete fixes so the same tactic won’t work twice.
Follow legal and compliance requirements
If data is exposed, understand your obligations. Follow applicable breach notification rules and communicate promptly and clearly. Straightforward updates help maintain trust.
How This Model Builds a Cybersecurity Strategy for Business
Using Left of Boom and Right of Boom gives you a complete plan: reduce risk up front, and be ready to respond. For many offices around Bay County, that means a steady rhythm—train people, apply updates, review access, test backups, and rehearse the response plan. If something happens, you already know who to call, what to isolate, and how to restore operations.
Frequently asked questions
Is Left/Right of Boom only for large companies?
No. Small and mid-sized businesses benefit a lot because the model keeps efforts focused on the essentials before and after an incident.
How often should we test our incident response plan?
At least once a year, and after any major change in your systems or team. Short tabletop exercises are a practical way to rehearse.
What are the first steps if we’re starting from scratch?
Begin with two-step login on key accounts, reliable backups, timely updates, basic security training, and a simple written response plan.
What’s the difference between backup and disaster recovery?
Backups are copies of data. Disaster recovery is the process and tools to restore systems and resume work using those copies.
If you want help building a two-pronged plan that fits your business, we’re here to assist. You can get in touch with Flux Labs, your local managed IT provider in Panama City.


